Personal Data Leaked After Companies Outsourced Customer Service and Employee Training…More Than 10 MetaM Clients Report Breaches, Data on 70,000 People Also Leaked at Samsung SDS Subsidiary
English translation of the original Korean report. Images and source documents may contain Korean text.
More Companies Report MetaM-Linked Data Breaches on the 20th…Personal Data Management at Outsourced Customer Service and Training Providers Under Scrutiny
Personal data breaches have occurred in succession at external service providers entrusted by companies with customer service and employee training.
The number of client companies reporting personal data breaches linked to the hacking of customer service outsourcing company MetaM has risen to more than 10. Meanwhile, personal information belonging to approximately 70,000 employees was also found to have been leaked earlier from an education platform operated by Multicampus, a subsidiary of Samsung SDS.
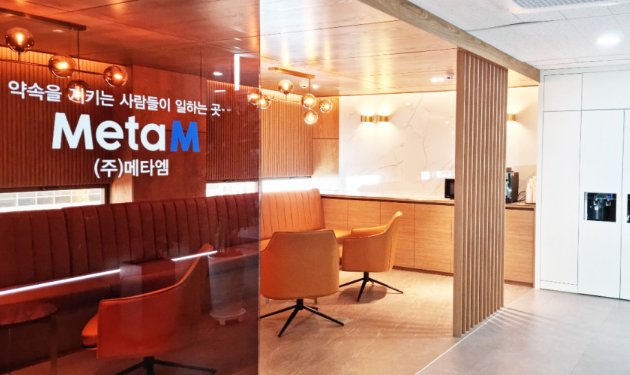
According to data submitted to the National Assembly on the 20th, the Personal Information Protection Commission (PIPC) received personal data breach reports from MetaM on the 14th and 15th. The number of companies reporting related breaches, including Coinone, Bungaejangter (Bunjang) and the operator of MEGA MGC COFFEE, which entrusted customer service operations to MetaM, is believed to have increased from three to more than 10.
MetaM provides outsourced customer service operations for approximately 200 companies across sectors including finance, distribution, manufacturing and information technology. The Korea Internet & Security Agency (KISA) is analyzing access logs related to the incident, while the PIPC is also conducting an on-site investigation. However, the client companies actually affected and the extent of the data leakage have yet to be determined.
A similar incident also occurred in the corporate employee training sector. On the 9th, unauthorized external access was detected in the cloud environment of ‘Learning Platform,’ an online education service operated by Multicampus, a Samsung SDS subsidiary. The company notified its client companies of the incident on the 11th and reported it to the PIPC.
The provisional scale of the breach is estimated at approximately 70,000 individuals. The leaked information reportedly included names, telephone numbers and email addresses, as well as department names, employee numbers, account IDs, job grades and positions. Information that could reveal companies’ internal organizational structures was also exposed, but the precise method of intrusion, final number of affected individuals and details of the damage suffered by each client company have not yet been confirmed.
■ From Customer Service to Employee Training…Management and Oversight of Personal Data at Outsourcing Providers Under Scrutiny
MetaM and Multicampus handle customer service and corporate training, respectively, but both process personal information belonging to multiple companies. Client companies remain subject to management and supervisory obligations under relevant laws even when they outsource operations, while outsourcing providers must also implement safeguards required by their contracts and applicable legislation.
Multicampus counts Samsung Electronics, Samsung Global Research, the Korea Chamber of Commerce and Industry, Samsung Life Insurance and Samsung SDS among its major clients. Samsung SDS is the largest shareholder, holding a 62.40% stake, but it has not been confirmed whether it directly managed cloud operations or security monitoring for the education platform involved in the incident. It also remains necessary to determine separately whether employee information belonging to these major client companies was actually leaked.
Personal data breaches involving outsourced education providers have occurred before. Last September, a hacking incident at online education platform provider Malgnsoft led to reports of approximately 2.37 million personal data records being leaked. Around 20 institutions and organizations, including the Anti-Corruption and Civil Rights Commission, were believed to have been affected.
Overseas, data breaches involving external service providers have also continued. On the 19th, JPMorgan Chase, Visa and Mastercard disclosed information breaches linked to cyberattacks targeting third-party service providers. JPMorgan Chase said that marketing information, including the names and email addresses of some customers, may have been accessed, while Visa and Mastercard said their core payment systems had not been affected.
The series of incidents has brought the security management systems governing companies that outsource personal data processing and the providers handling that information under closer scrutiny. Both MetaM and Multicampus will need to establish the methods of intrusion and the extent of the damage, while also determining whether access permission management and security inspections were adequate before the incidents and whether notifications to client companies and measures to prevent harm were sufficient afterward.